About
For the longest time, I wasn't sure what I wanted to do. There were so many fascinating fields. I drifted from one interest to another, but one thing never changed: my love for learning and figuring out how things work.
At some point, I realized there was simply no perfect answer. I had to choose a path that aligned with my values. The world is becoming increasingly dependent on technology, and organizations must adapt to stay competitive and serve their customers better. That means maintaining smooth IT operations so people can work with fewer disruptions, securing data and infrastructure against a growing threat landscape, and leveraging the cloud to innovate and scale. It also means automating workflows and using data to support better decisions. To me, these aren't just technical challenges, they are opportunities to create real impact for both businesses and the people who depend on them.
This portfolio reflects my commitment to continuous learning through hands-on labs and projects, even with limited resources. With each project, I hope to develop practical skills that help organizations build, secure, and improve their technologies as they achieve their digital transformation goals.
Knowledge Areas
No tags yet for this specialization.
Projects and Blogs
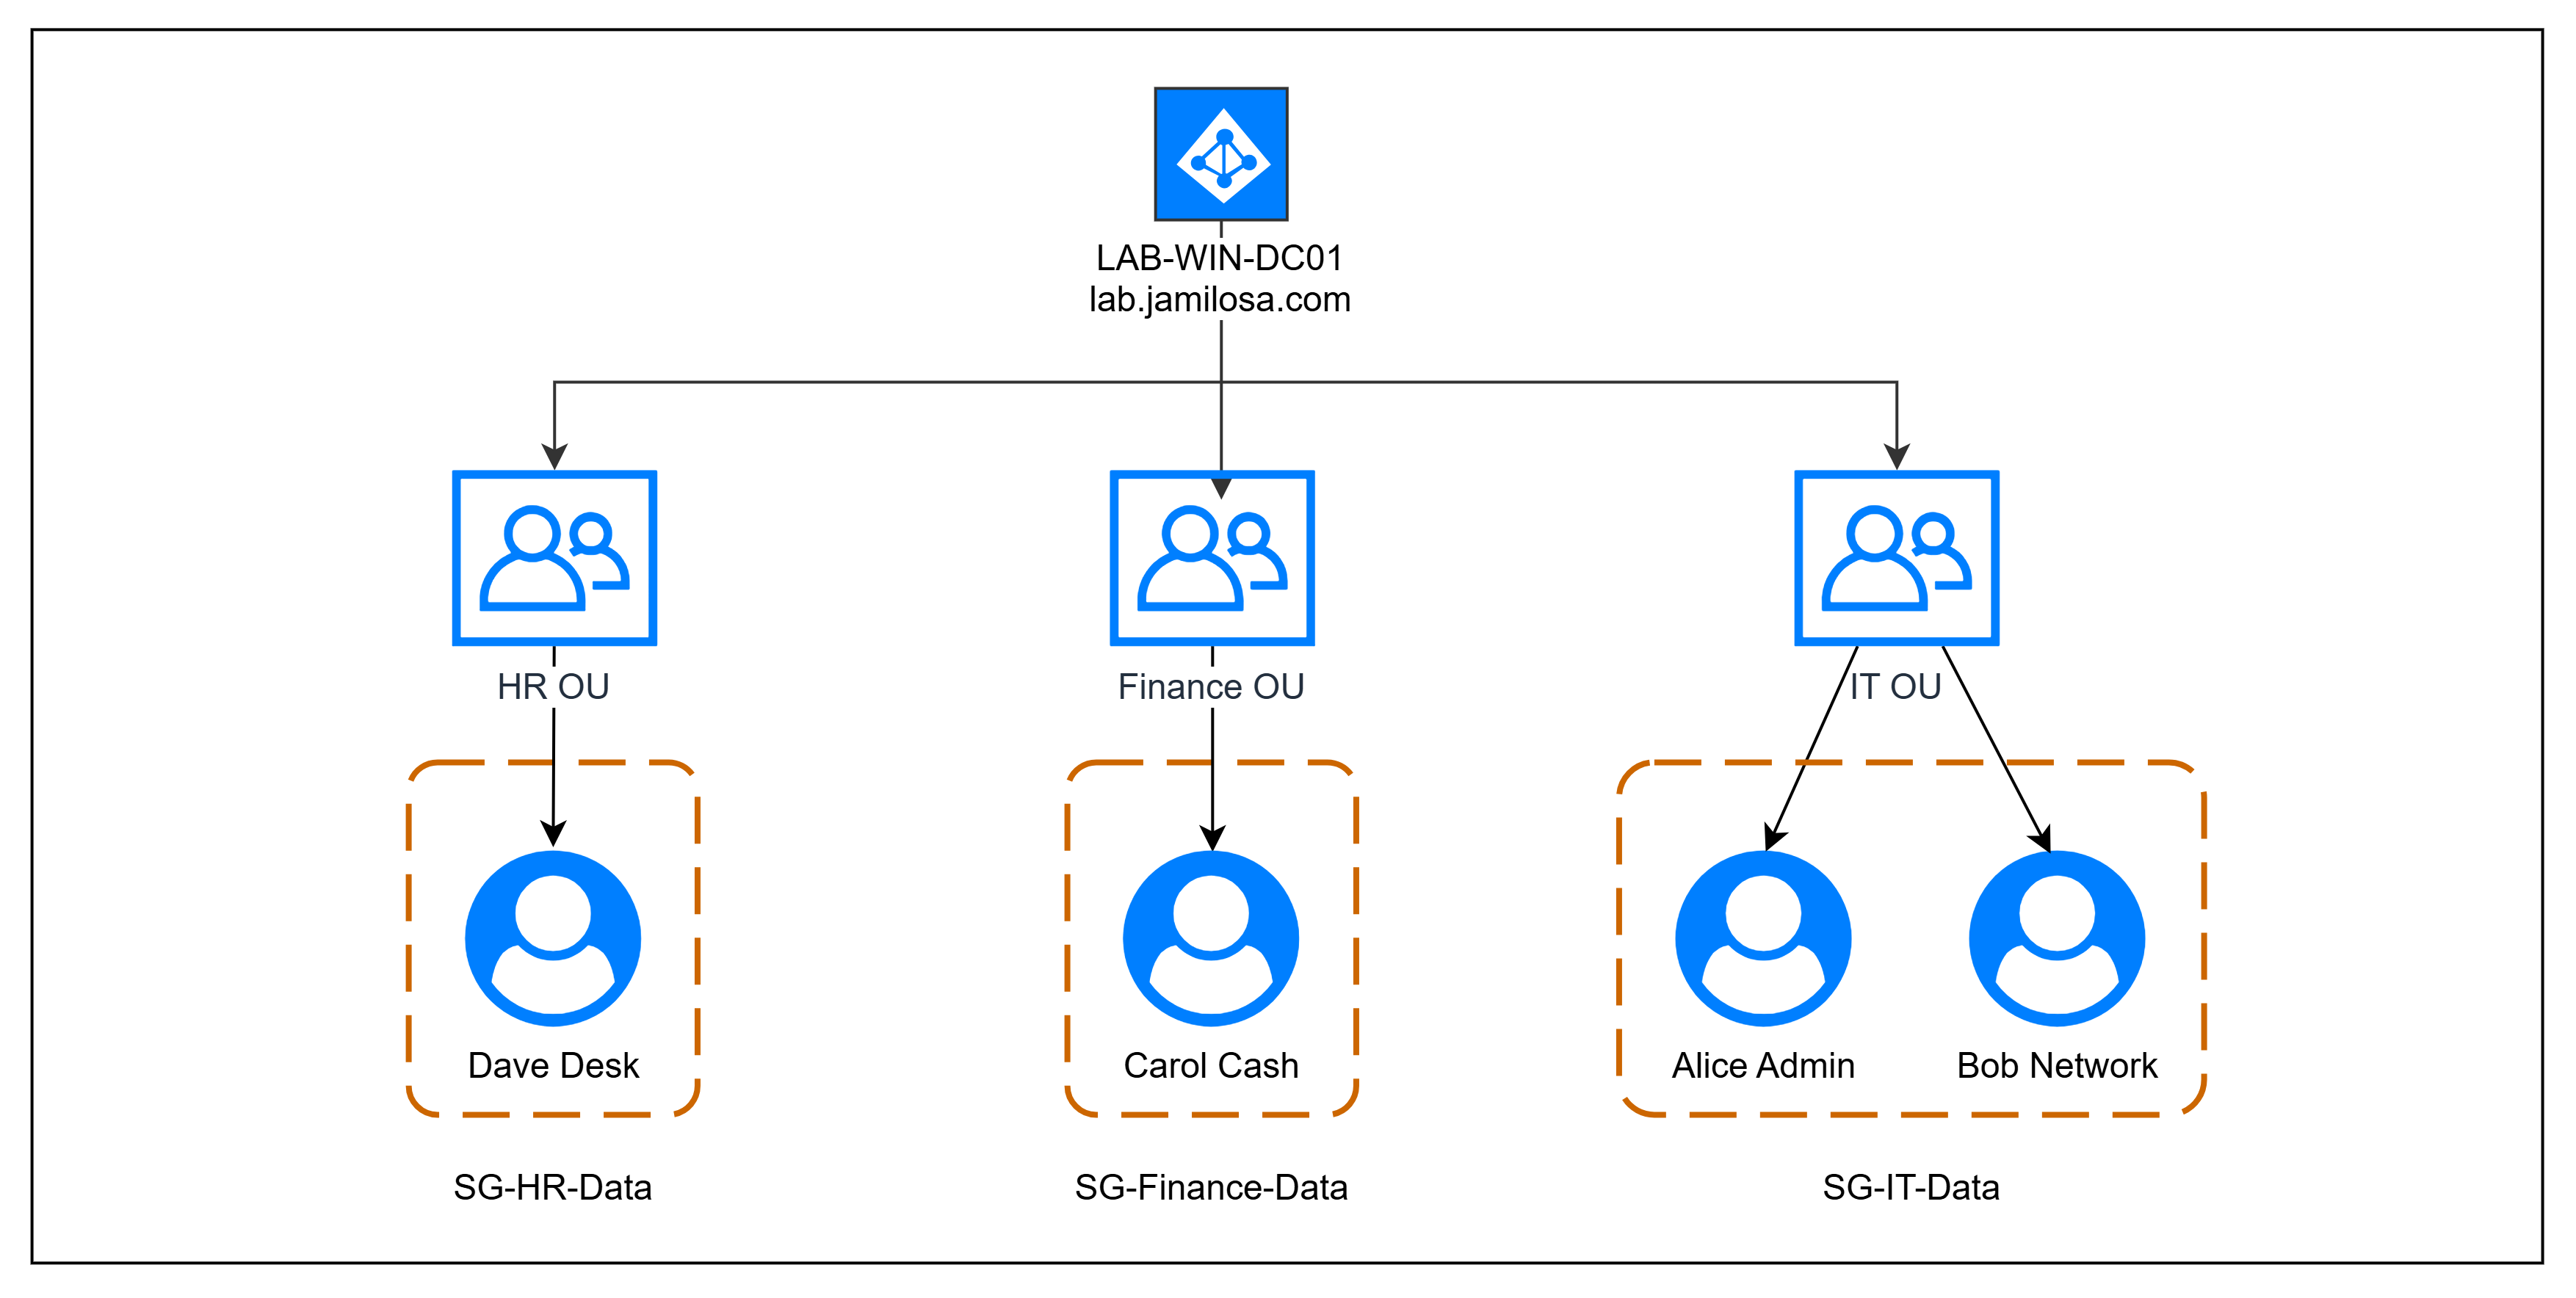
Deployed an Active Directory Domain Services environment on Windows Server 2022 for centralized identity and resource management. Automated user provisioning and departmental access with PowerShell, enforced endpoint policies through Group Policy, and integrated Wazuh and Sysmon for centralized security telemetry.
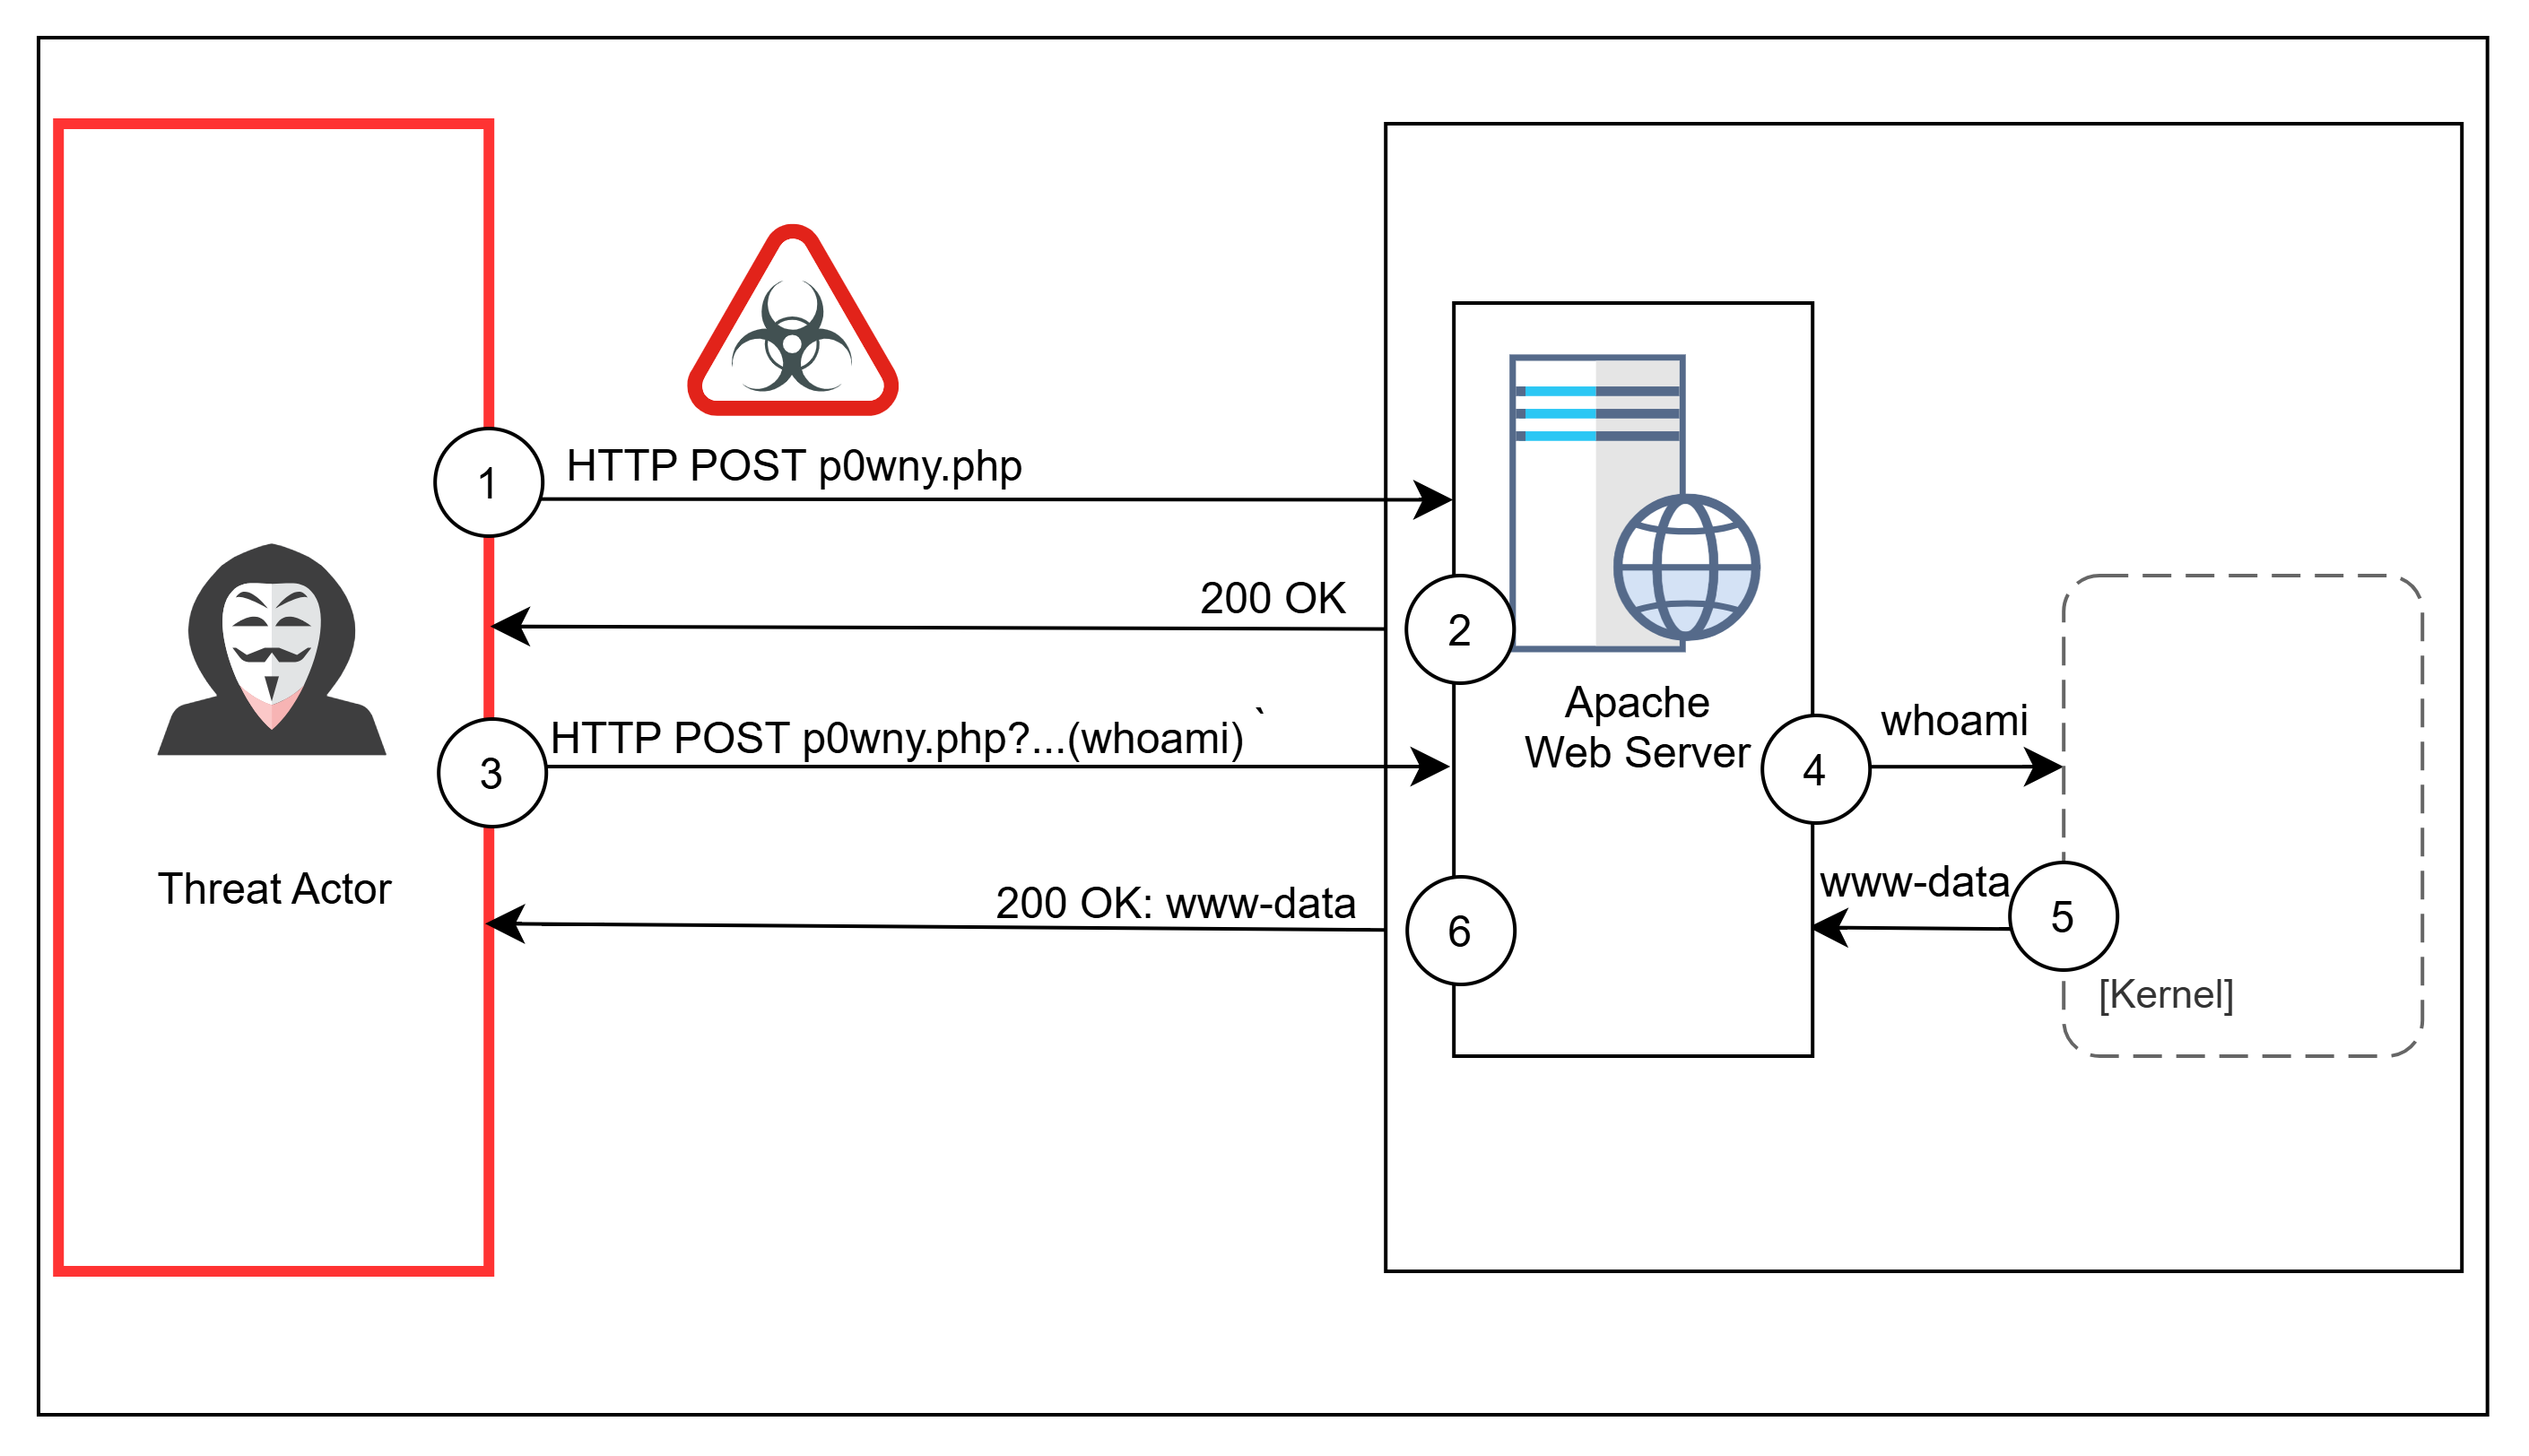
Investigated a simulated Remote Code Execution (RCE) incident on a Linux web server by correlating Wazuh alerts and analyzing raw Auditd telemetry to uncover hidden HTTP POST payloads. Mapped the adversary's complete execution chain, from initial web vulnerability exploitation to database destruction.
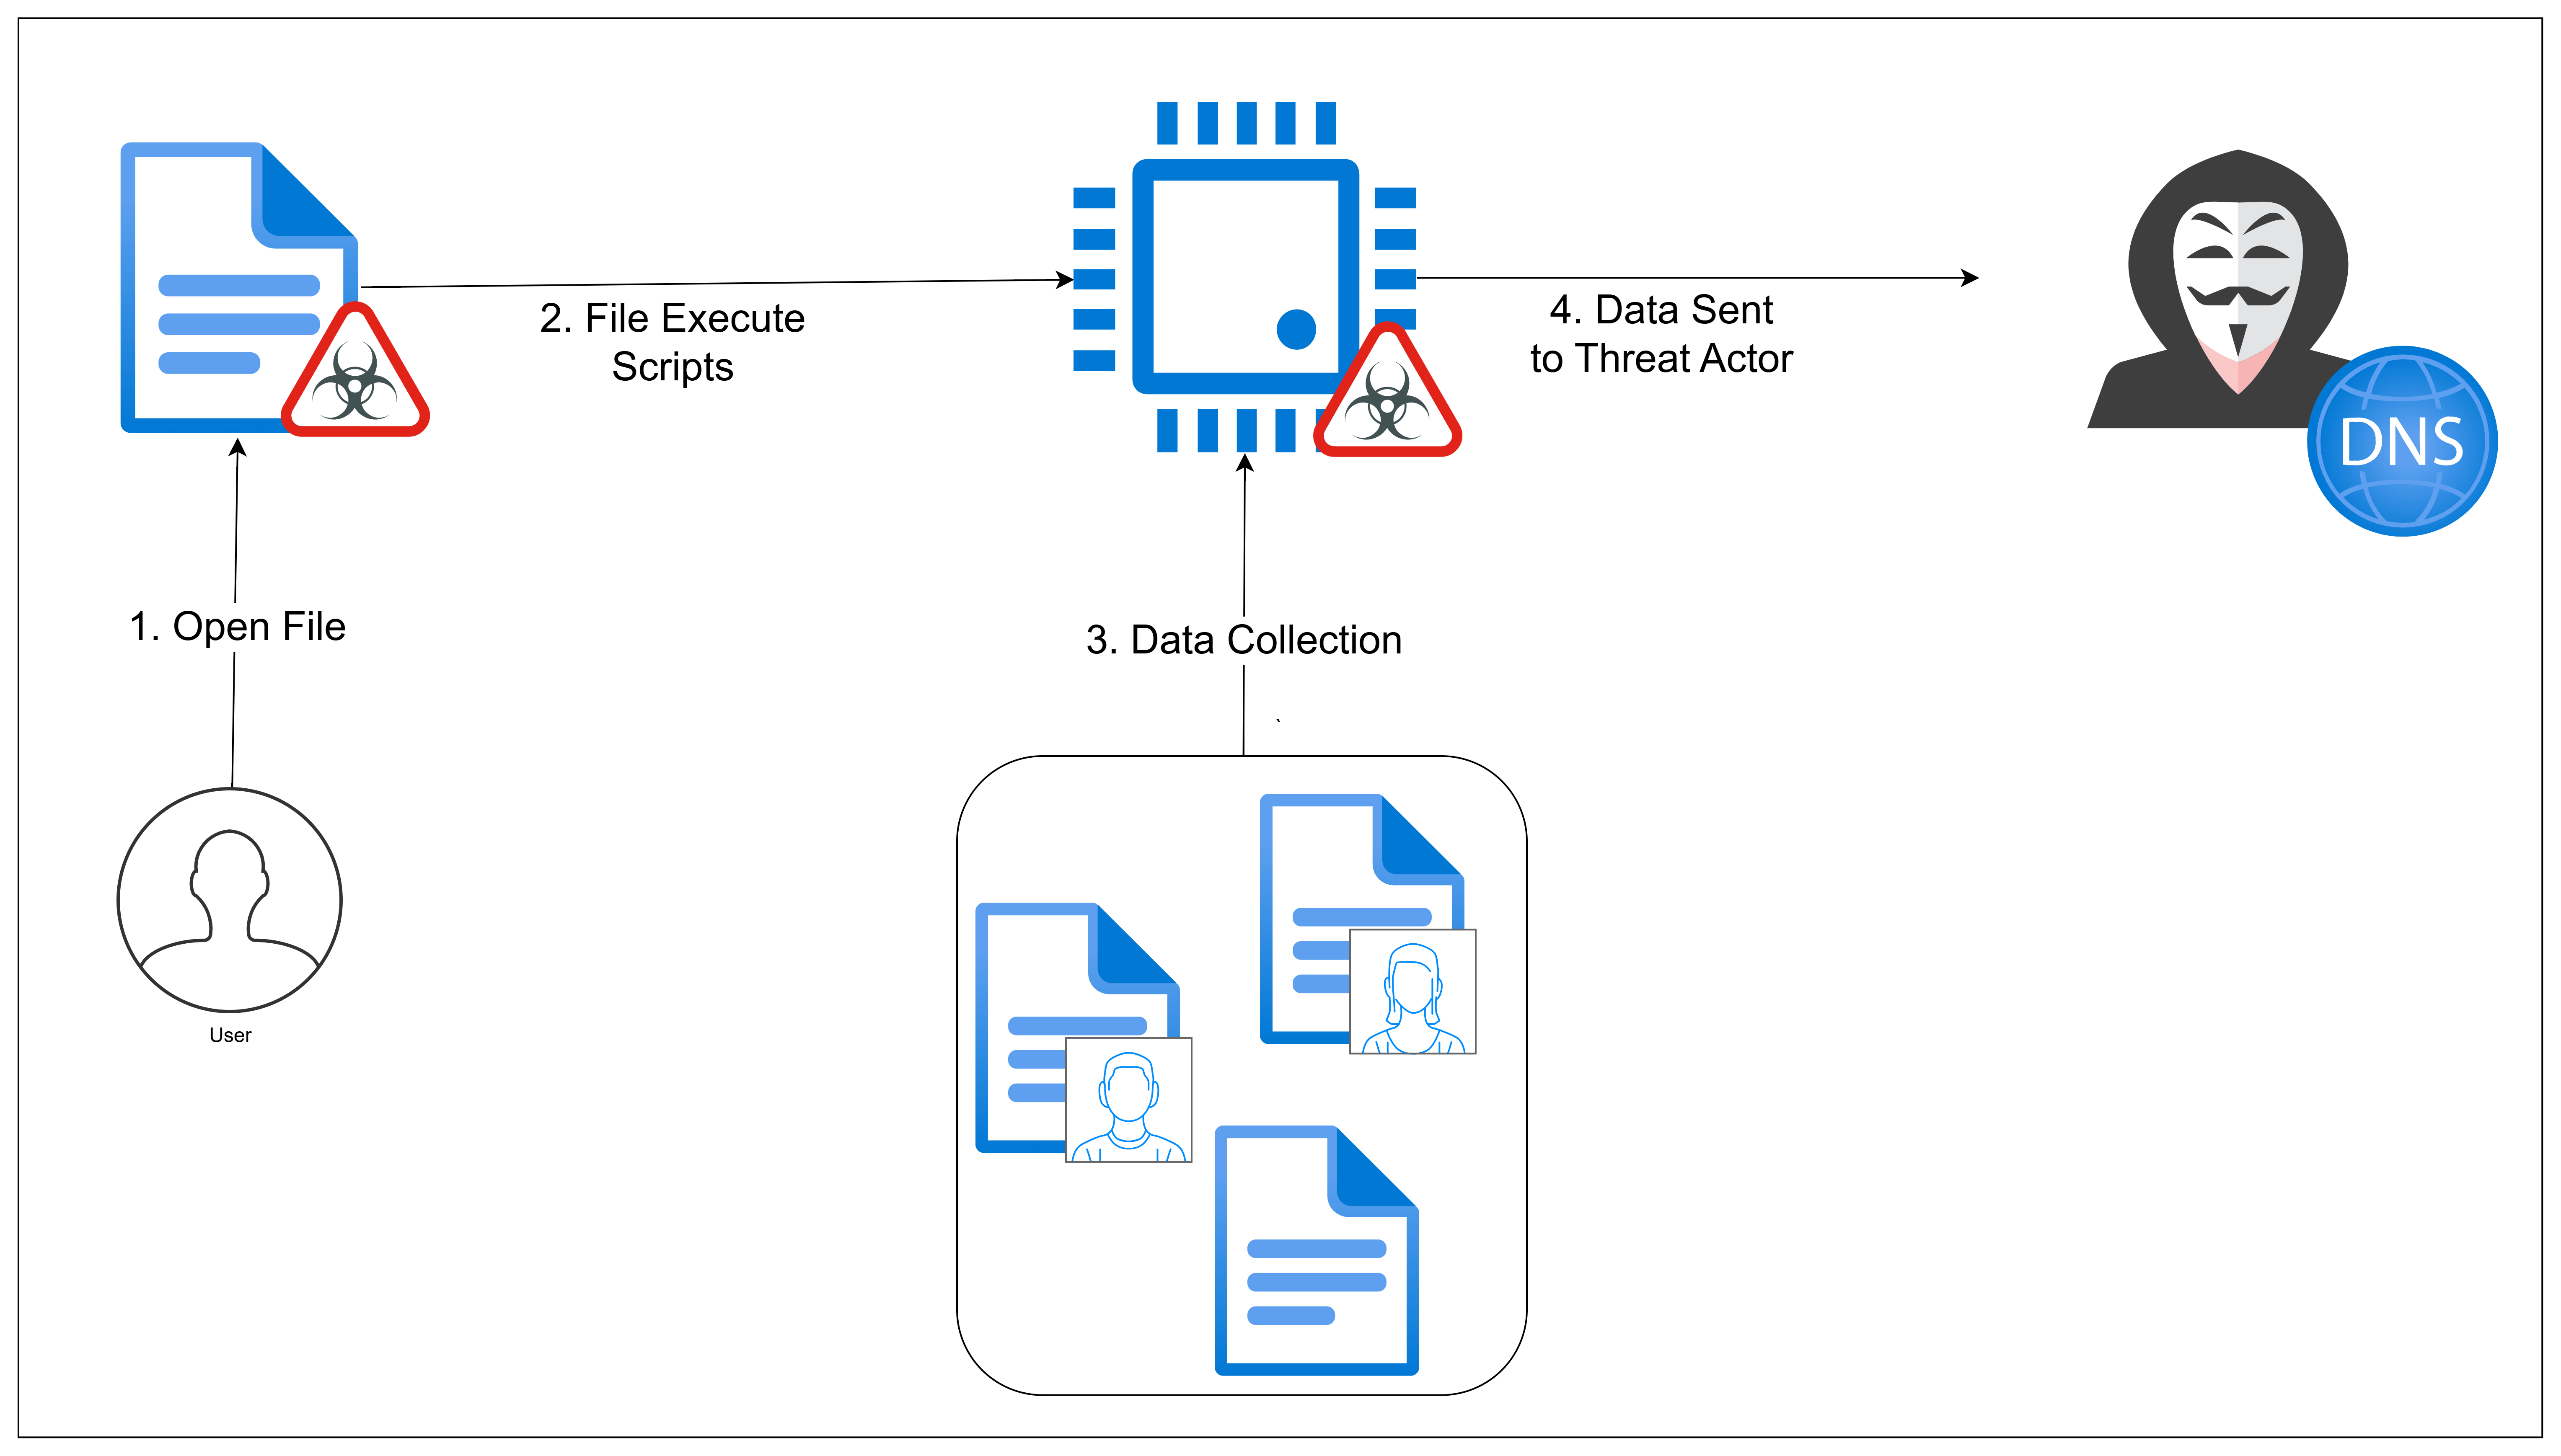
Investigated a simulated DNS exfiltration incident on a Windows endpoint by correlating Wazuh events and extracting manual artifacts via Sysmon and PowerShell Script Block Logging. Mapped the adversary's complete execution chain to the MITRE ATTACK framework.
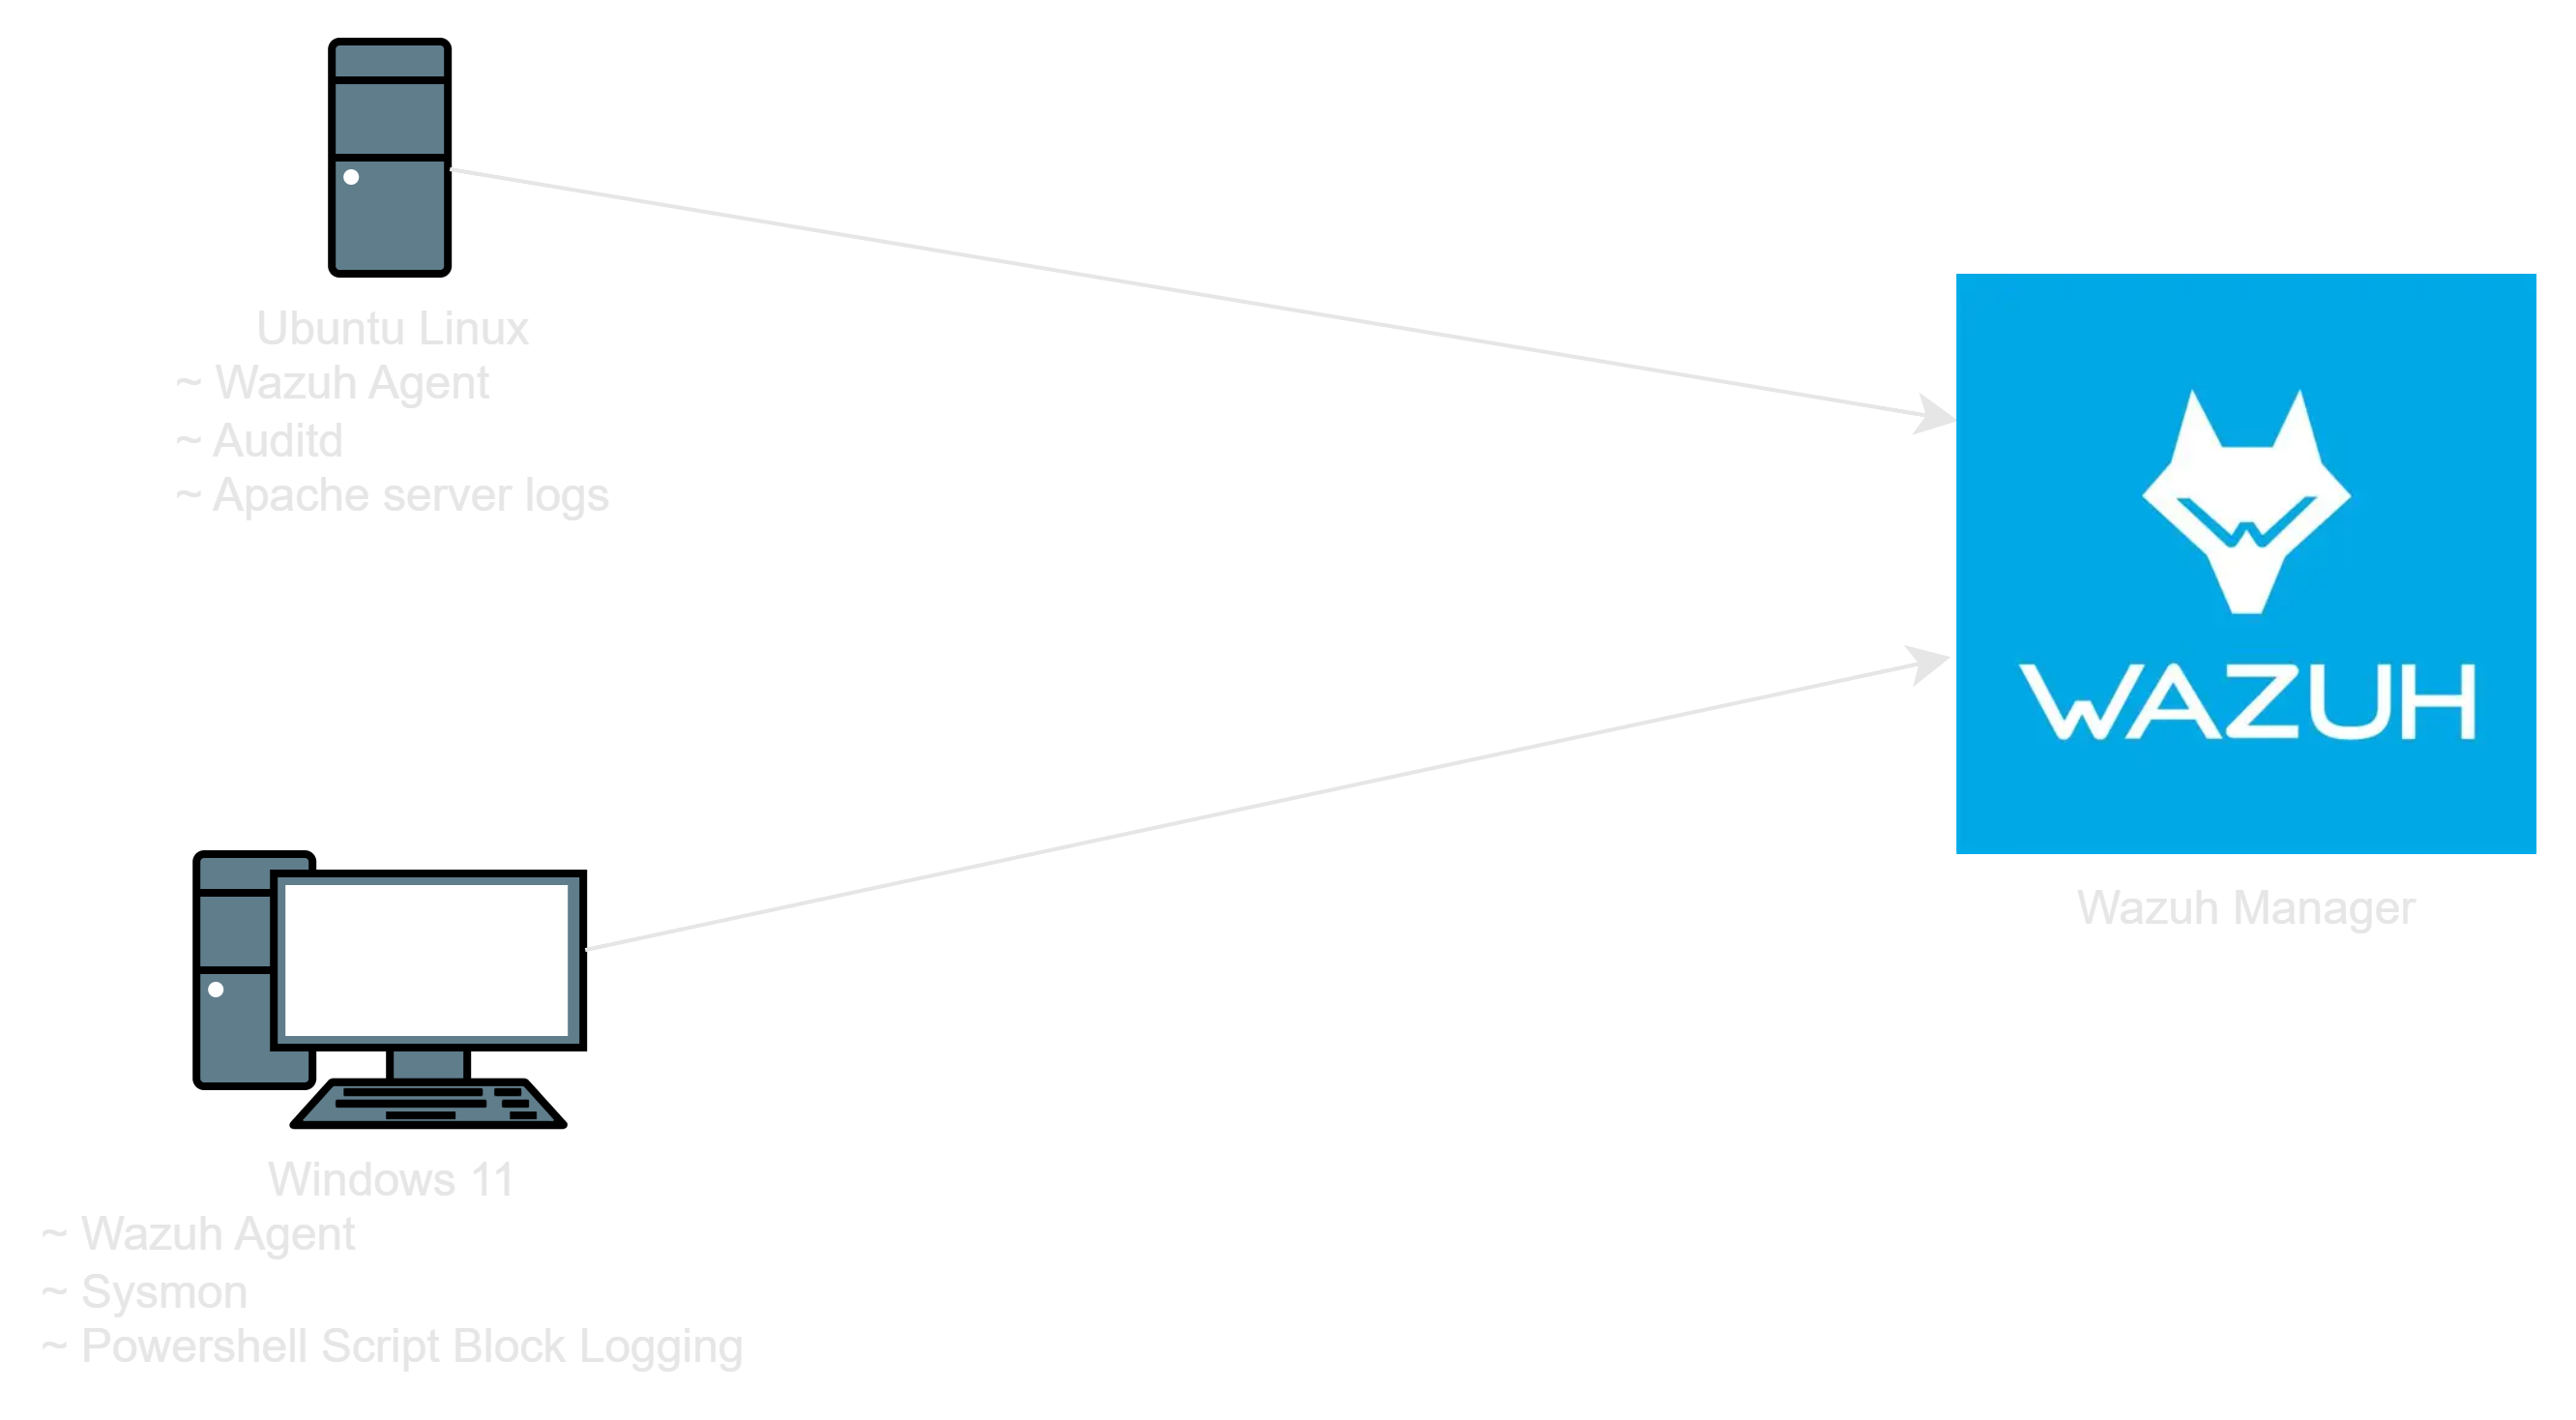
Deployed Wazuh Agents with Sysmon, PowerShell Script Block Logging, auditd, and Apache for endpoint and application telemetry. Validated process, file, command, PowerShell, and web request visibility during simulated attack activity.
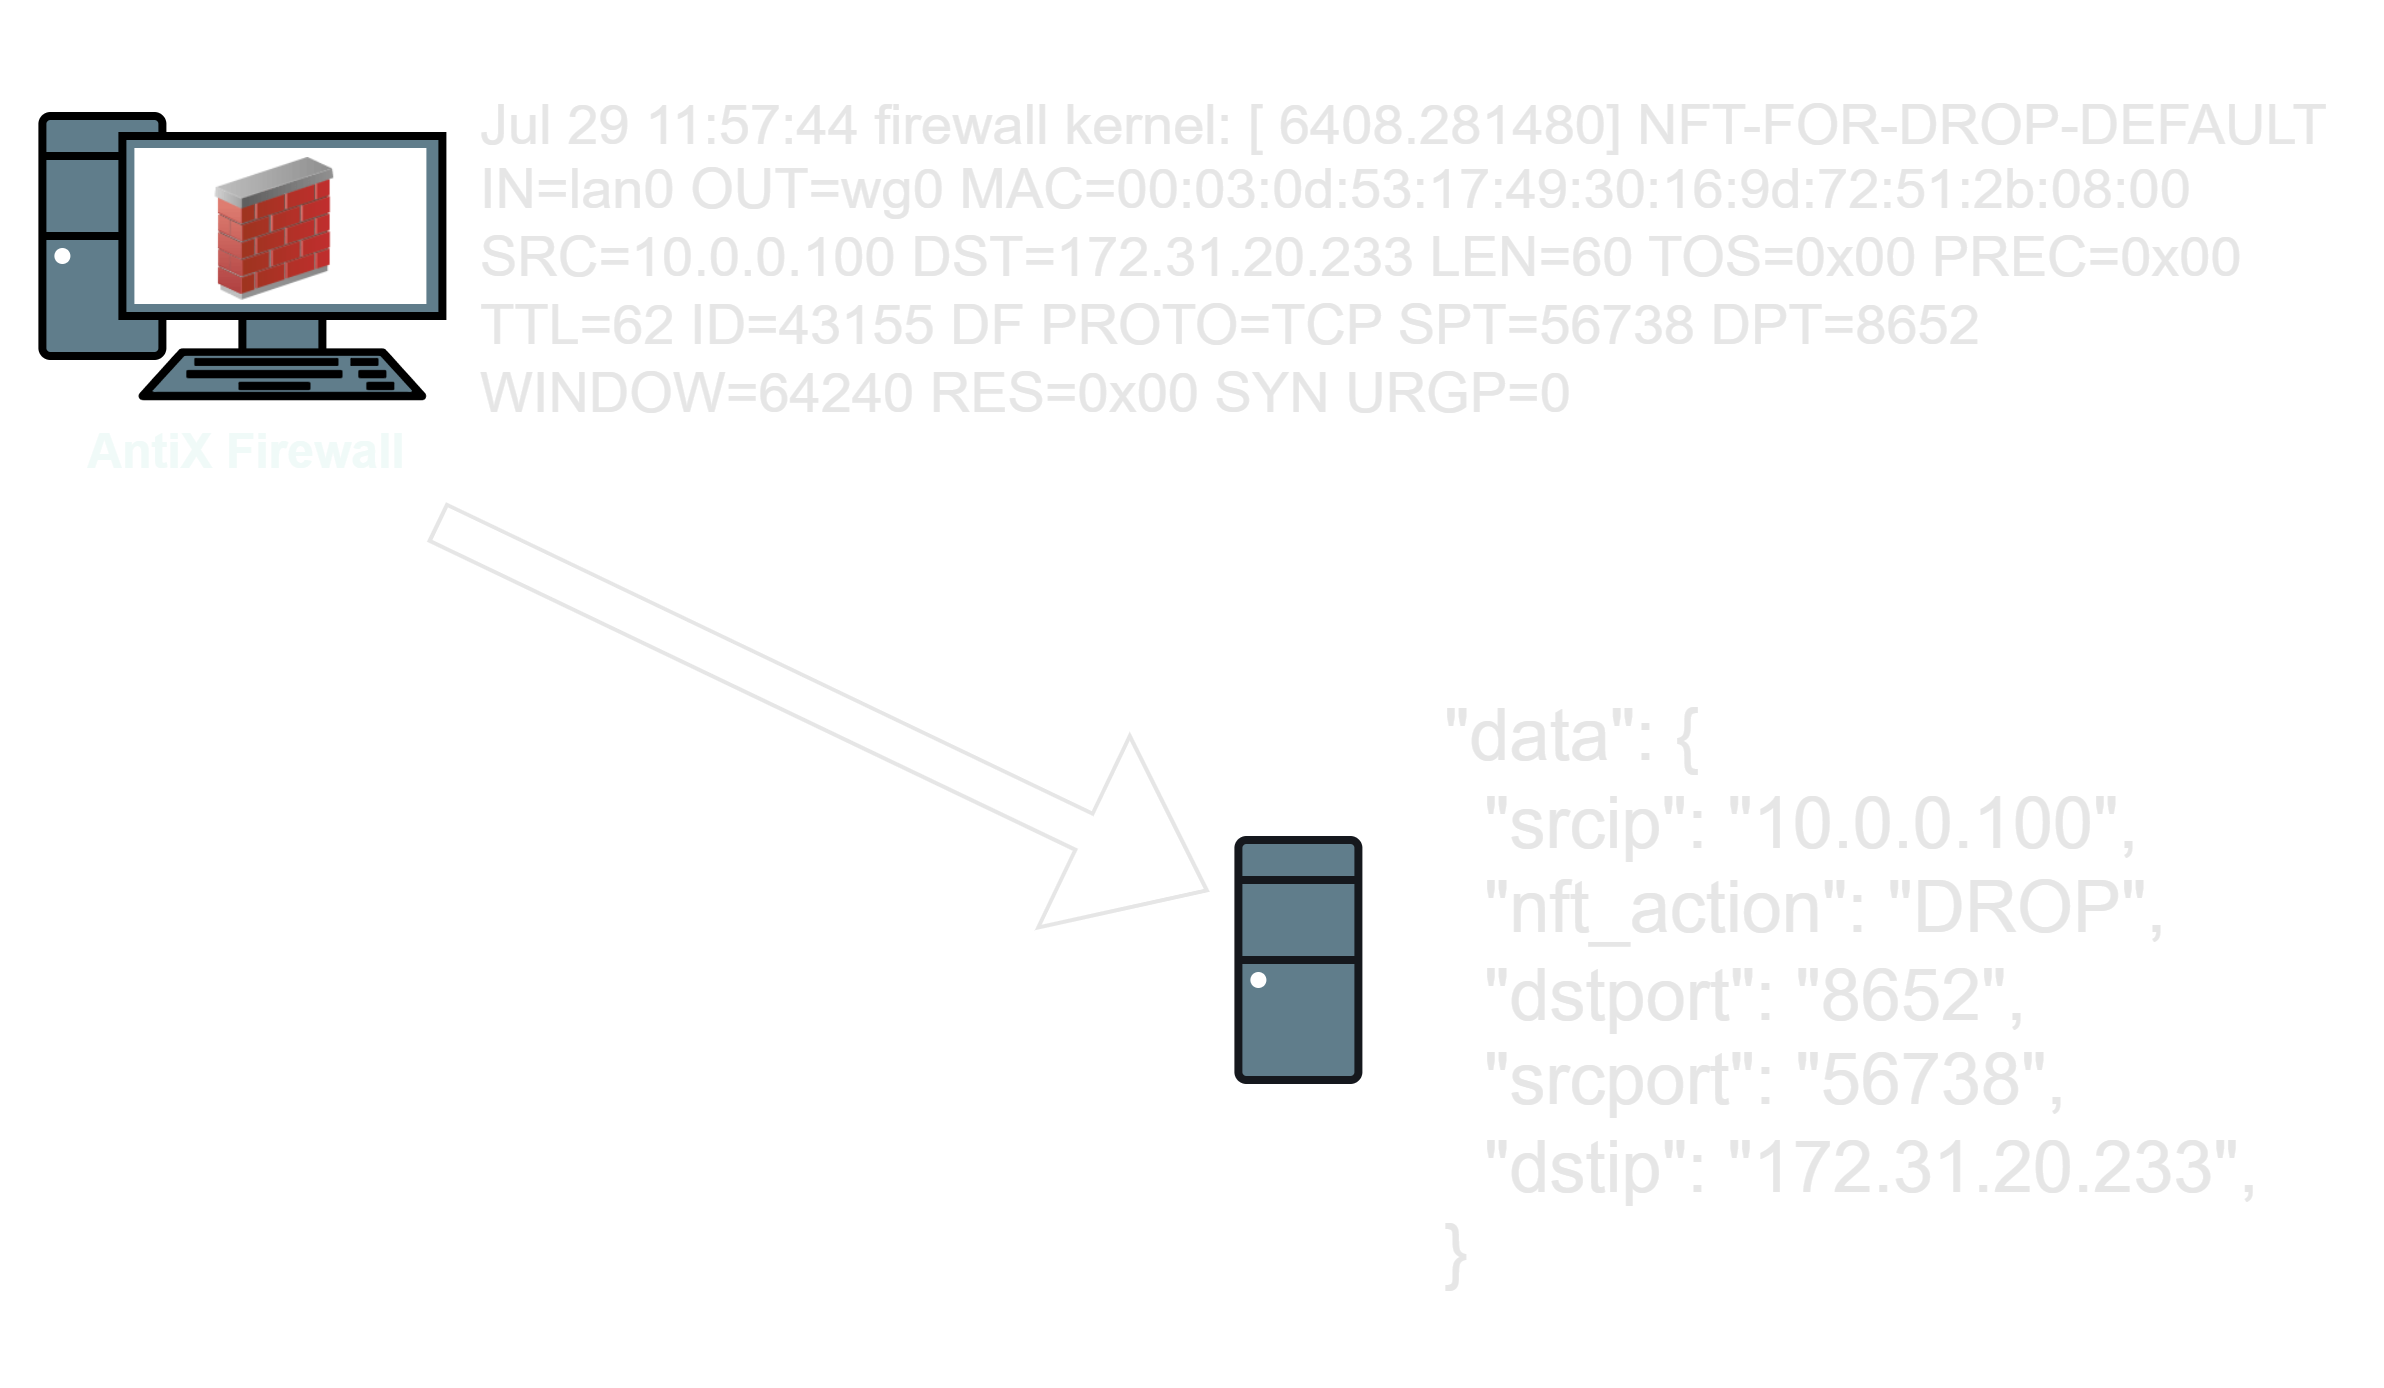
Built custom Wazuh decoders using PCRE2 to parse nftables and dnsmasq telemetry, then developed behavioral detection rules for suspicious DNS activity, spoofed traffic, and network reconnaissance. Validated the detections through controlled attack simulations and mapped relevant rules to MITRE ATTACK.
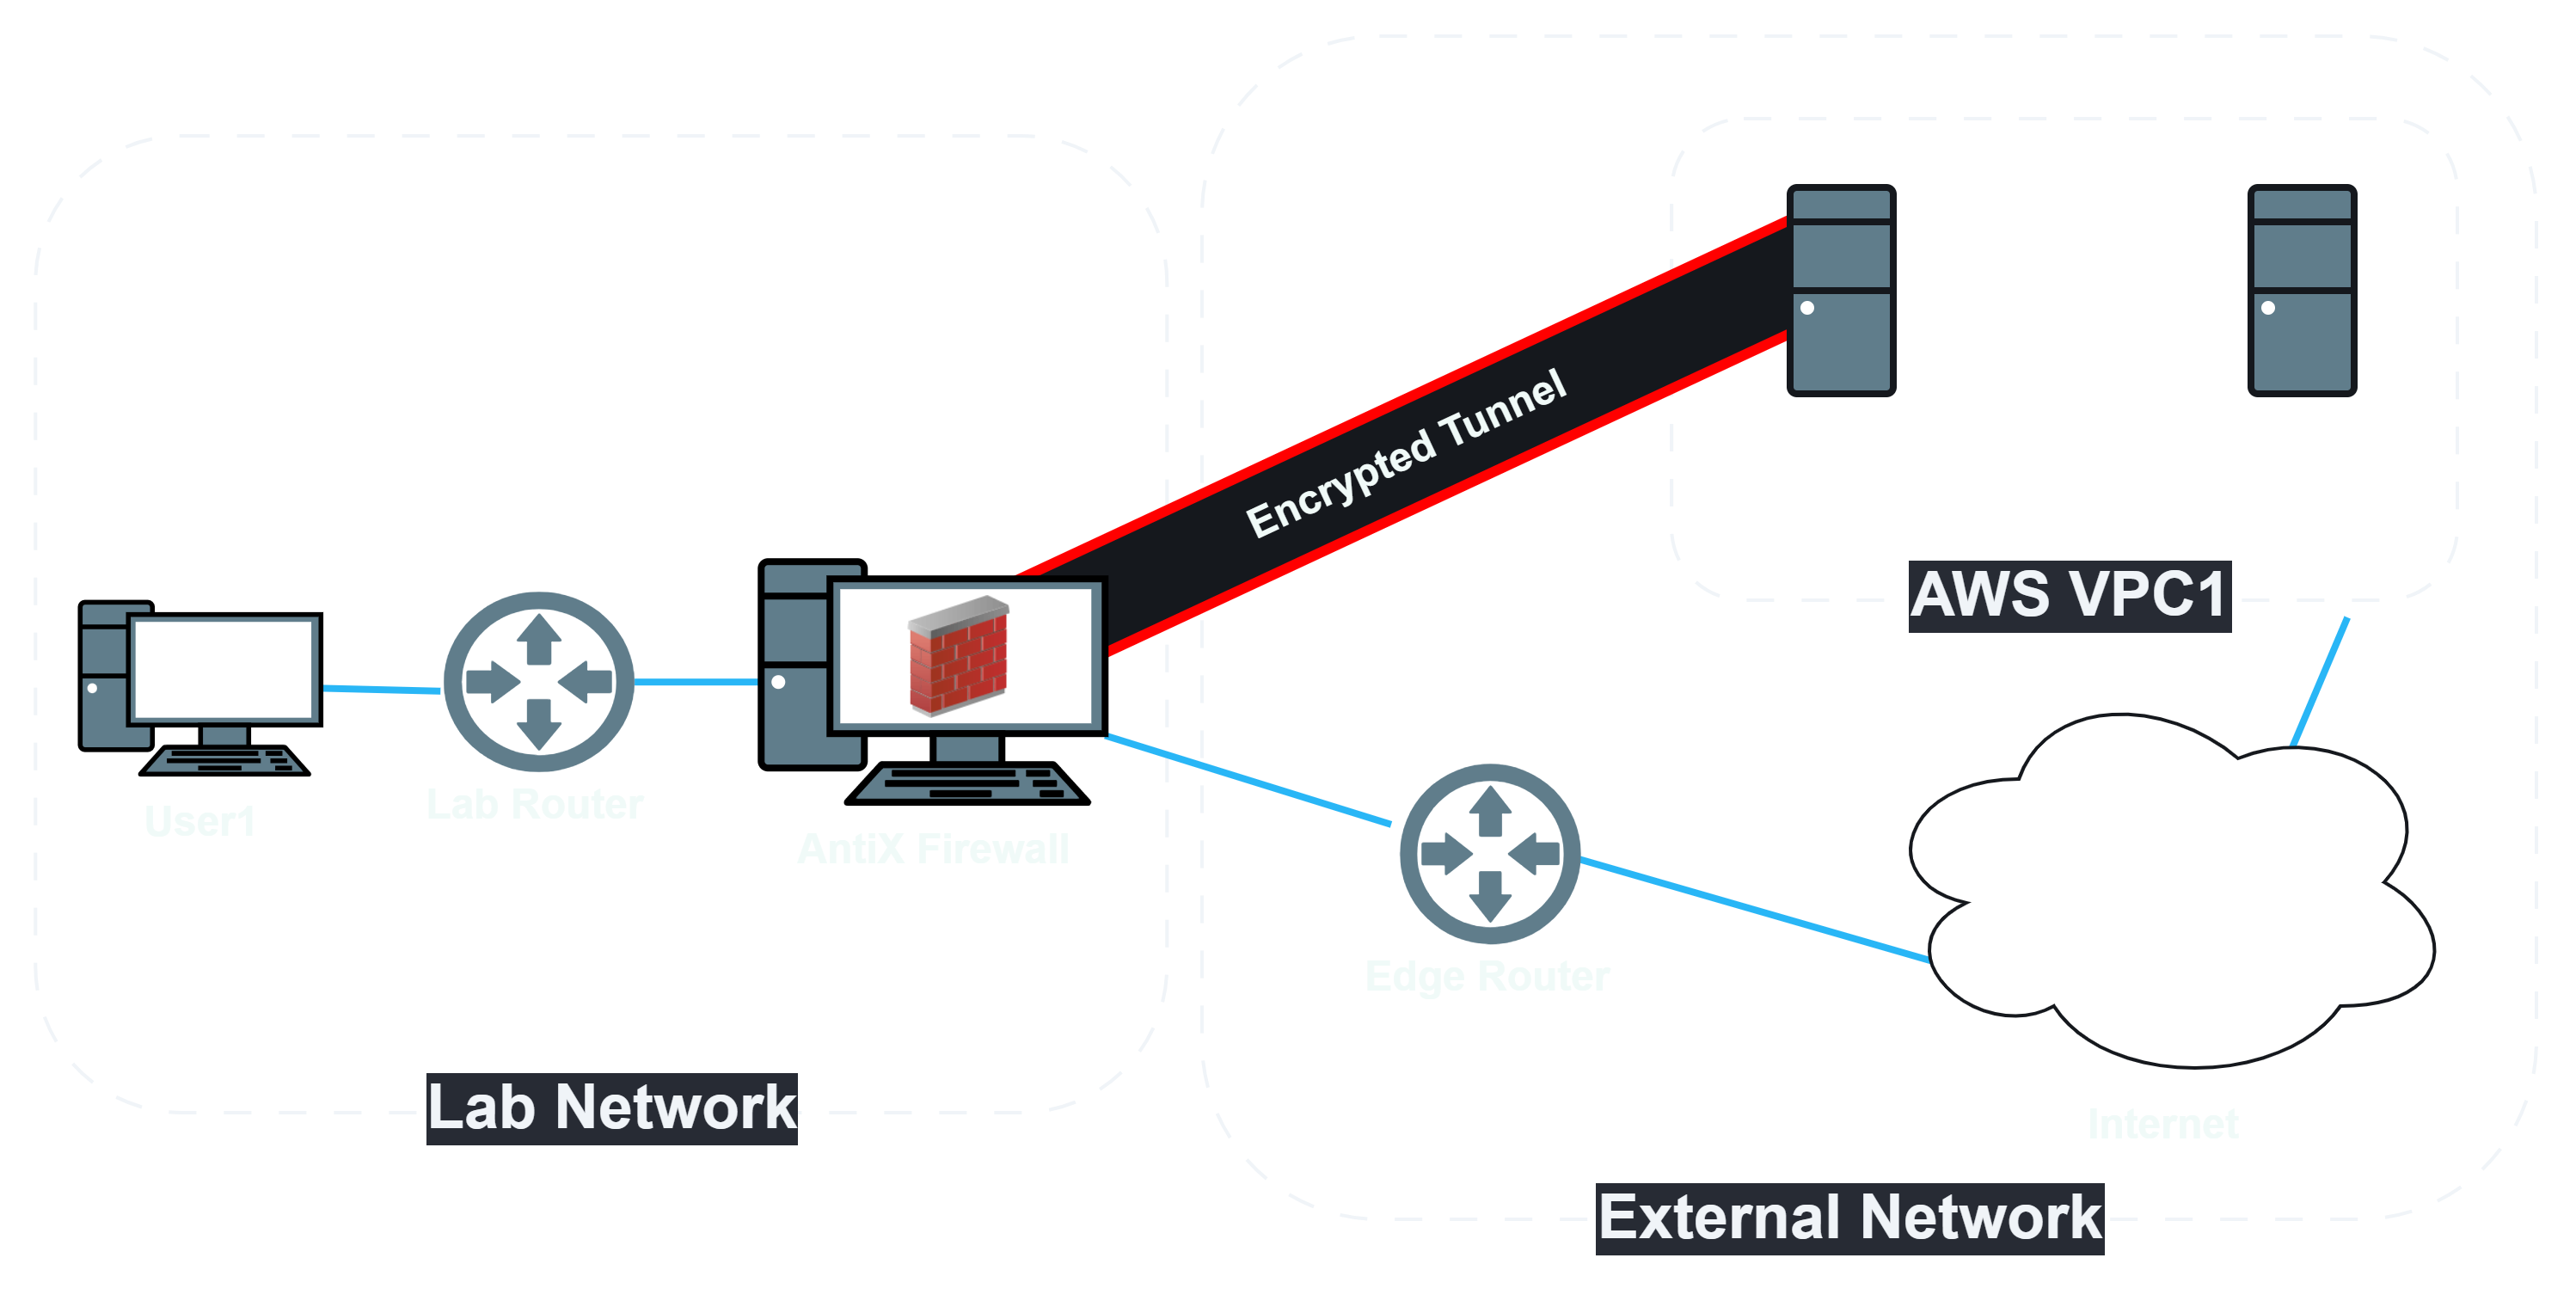
Integrated the home lab with AWS by deploying a site-to-site WireGuard VPN, configuring VPC routing, Security Groups, and nftables to securely extend the lab into a cloud environment.
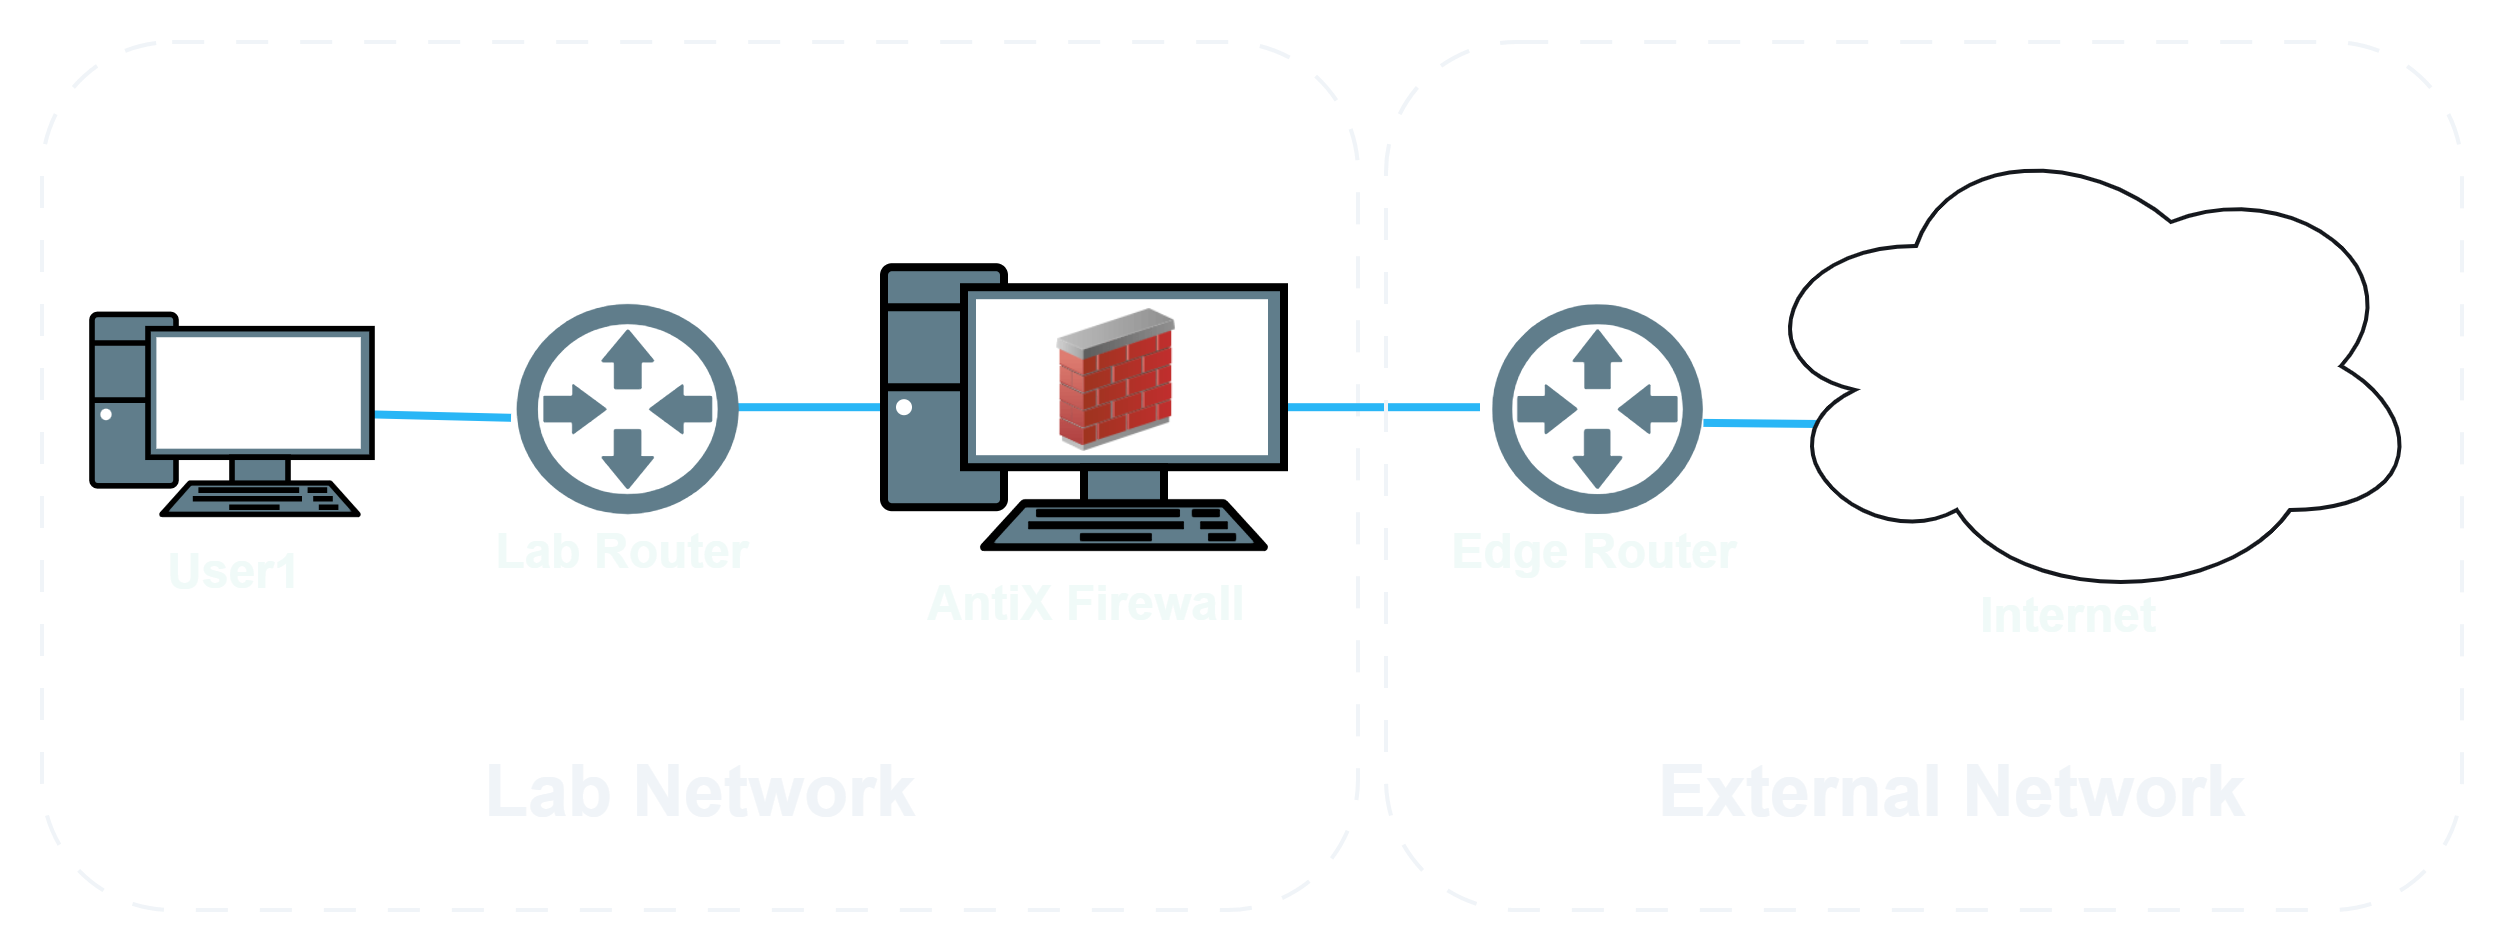
Repurposed a retired 32-bit laptop into a Linux-based firewall for a small cybersecurity lab. Using AntiX Linux, nftables, dnsmasq, rsyslog, and logrotate, the firewall provides network address translation (NAT), stateful packet filtering, DNS sinkholing, and centralized logging.